Most XRP losses are not ledger failures. They are key-management failures. A mnemonic phrase is the master backup for many modern XRP wallets, and offline signing is how you authorize a payment without placing that backup on a networked computer. This guide explains how to confirm a backup is real, how to keep signing air-gapped, and which everyday habits actually reduce risk.
What You Are Protecting
On the XRP Ledger, control of an account means control of a secret that can produce valid signatures for that account's address. Wallets package that secret in different ways:
- A BIP39 mnemonic, usually 12 or 24 words, used by many software and hardware wallets
- A native family seed, often beginning with the letter
s - A key held inside a hardware wallet or secure element, where the seed is not meant to leave the device
A mnemonic is not a password that support staff can reset. Anyone who learns the words, in the correct order, can usually recreate the keys and move the XRP. Optional passphrases, sometimes called a 25th word, change the derived account entirely. Verification and offline signing exist to answer two questions: Is this backup correct? and Can I approve a transfer without exposing the secret to the internet?
Verify the Phrase Before You Need It
People usually discover a bad backup after a phone dies, an app is removed, or a device is replaced. Check the phrase while you still have a working wallet and no urgency.
A safe verification sequence:
- Identify the backup format first. Confirm whether you hold a BIP39 word list, a family seed, or a hardware-wallet recovery phrase. A phrase that looks plausible can still be the wrong format for the account you think it restores.
- Check words against the official list. Standard BIP39 English words come from a fixed list. If a word is not on that list, it was misheard or miswritten. Consult a copy you already trust, ideally offline. Do not paste words into a website to "look them up."
- Compare the derived address, not the private key. On a device you control, restore or check the backup only far enough to derive the account address, then match that address to the one you already use. A matching address is the useful proof. You do not need to display or export private keys to finish the check.
- Stay on a trusted, offline path. Use the wallet's own verification flow, a hardware wallet's recovery check, or well-known open-source software that you run locally. Disconnect Wi-Fi and Bluetooth before the phrase is entered. A computer that merely has its browser closed is not offline.
- Make the durable copy only after the check succeeds. Write or stamp a second copy from a phrase that has already matched your address. Store that copy apart from your daily devices.
Never do this:
- Type the phrase into a browser, a support chat, a stranger's QR tool, or any page that offers to validate, sync, or unlock a wallet
- Photograph it, or save it in cloud notes, email, or screenshots
- Run the check on a borrowed, workplace, or public computer
- Read the words aloud to anyone who claims to be exchange, wallet, or "recovery" support
Phishing sites are designed to look like verification tools. A legitimate check never requires you to send the phrase to a server. If a message says the account will be frozen unless you re-enter the words, treat that urgency as the attack. The ledger does not seize personal accounts because a website was ignored.
How Offline Signing Should Work
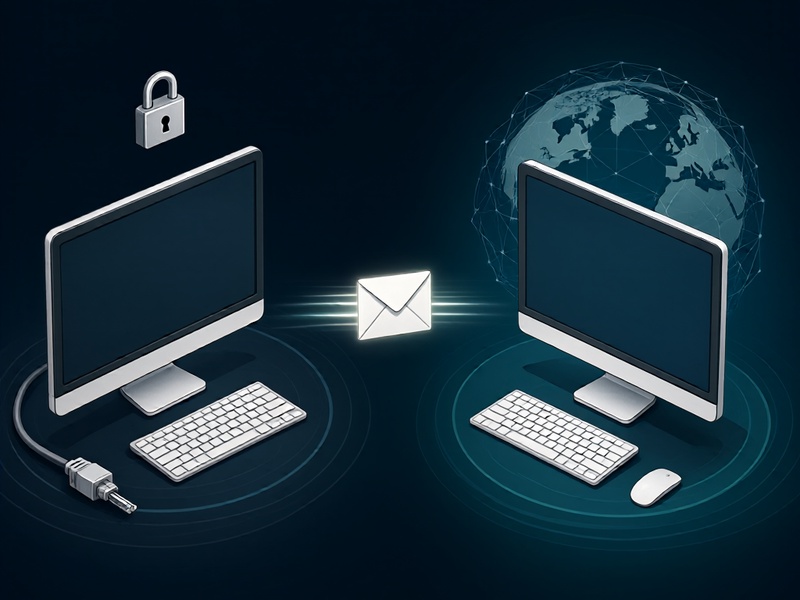
Offline signing separates authorization from broadcast. The secret stays on a machine or device that cannot reach the network. A second, online machine receives only an already-signed transaction and submits it.
Two roles, two machines
- Air-gapped signer: holds the mnemonic or hardware key, reviews the payment, and signs. It has no Wi-Fi, Bluetooth, or network tether while secrets are present.
- Online broadcaster: checks balances and account sequence, may prepare unsigned details, and submits the signed payload to a trusted endpoint or your own node.
A clean sequence
- On the online machine, write down only non-secret details: destination address, amount, fee expectation, account sequence, and destination tag if one is required. Tags matter. Sending to a shared exchange address without the correct tag can leave funds where you cannot retrieve them by simply "trying again."
- Move only that unsigned information to the signer. A QR code of an unsigned transaction, or a text file on removable media used in one direction, is enough. Never move the mnemonic toward the online machine.
- On the signer, read the human-readable fields before signing: source, destination, amount, fee, sequence, and tag. If any field disagrees with your notes, stop.
- Sign locally and export only the signed transaction.
- On the online machine, submit that payload. After a valid signature exists, the secret is not needed again for that payment.
- Confirm the transaction result through a source you trust, then delete temporary files on both machines.
A hardware wallet is a narrower version of the same idea: the seed stays in the device, and the computer sees a signature rather than the words. The review habit still matters. Read the device screen, not only the computer screen. Clipboard malware and lookalike addresses are aimed at the moment between copy and confirm.
Details That Change the Outcome
- Use a dedicated signer. A spare machine that never browses is safer than "offline mode" on a daily laptop. Malware can wait until you disconnect the network and then capture what you type.
- Install software from a known source. Prefer the wallet vendor's official release or a widely reviewed open-source build. Check published checksums when they exist. Skip unofficial "XRP offline signer" downloads found through ads or random links.
- Prefer one-way transfer. QR codes of unsigned, then signed, data reduce the chance of carrying a malicious file back onto the signer. If you use a USB drive, reformat it and do not allow automatic execution.
- Treat passphrases as part of the backup. If you enabled an optional BIP39 passphrase, the 12 or 24 words alone will restore a different account. Record that a passphrase exists, store it separately from the words, and verify the combination by matching the address.
- Include every ledger field. Offline signing still has to respect account sequence, fees, destination tags, and any regular-key or multi-signing setup you have enabled. A carefully produced signature cannot fix a missing tag or a stale sequence.
- Store the backup physically. Paper fades, smears, and burns. Steel backups resist fire and water better, but only if the stamping is legible. Keep two copies in separate places. A photo of the plate is not a second copy; it is an online leak waiting for a cloud sync.
Failures Worth Recognizing
You do not need an attack manual to avoid the patterns that drain accounts:
- Fake verification pages and browser extensions that ask for the 12 or 24 words
- Remote-support calls that coach you to "confirm ownership" by reading the phrase
- Address-swapping malware that changes a destination at paste time
- Malicious QR codes that encode a lookalike address or an unexpected payment
- Lookalike apps whose names sit one letter away from a known wallet
The common thread is a request for the secret, or a rush that keeps you from reading the signing screen. Decline both.
Checklist
- I know whether my backup is BIP39, a family seed, or a hardware recovery phrase
- I have matched the derived address to my real account on an offline or hardware device
- The phrase is not in photos, email, or synced cloud notes
- If I use a passphrase, it is recorded separately and included in the address check
- The signer has no network connection while it holds the secret
- I review destination, tag, amount, fee, and sequence on the signing device
- I submit only the signed transaction from the online machine
- A second physical copy sits in another location
- I will not type the phrase into any website, including one that claims to verify it
Closing
Mnemonic verification is a calm check that your backup reproduces the account you already control. Offline signing is the habit that keeps that backup from becoming an internet-facing secret. Neither practice requires theatrics. They require the right format, an address match, a signer that cannot reach the network, and a hard refusal to hand the words to any page, person, or app that asks for them.
Protect the phrase. Sign away from the network. Broadcast only what is already signed.