Restoring a wallet is the single most dangerous moment in a crypto user's life. Your entire net worth collapses into a short string of words that must pass through a screen, a keyboard, and an operating system — all of which may be compromised. Secure chip verification exists to close that gap. Instead of trusting software, the recovery process is anchored to a tamper-resistant piece of silicon that never reveals its secrets.
This guide explains what secure chip verification actually does during wallet restoration, how the flow works step by step, and where it still falls short.
Why Wallet Recovery Is the Weakest Link
When you restore a wallet, the seed phrase (or private key) must be entered in plaintext. That creates a chain of exposure:
- Clipboard and screenshot leaks — many users copy the phrase instead of typing it, exposing it to every app with clipboard access.
- Keyloggers and malicious input methods — compromised keyboards capture every keystroke, including your 12 or 24 words.
- Weak randomness — software pseudo-random generators can be biased, making derived keys easier to brute-force.
- Memory scraping — the seed lives in RAM while the app decrypts and derives keys, where any process with debug rights can read it.
- No proof of authenticity — a fake app or a malicious recovery tool can silently harvest everything you enter.
Secure chip verification addresses each of these by moving the sensitive steps into hardware that the operating system cannot read or modify.
What Counts as a "Secure Chip"?
The term covers several related technologies, and the differences matter:
- Secure Element (SE) — a dedicated, tamper-resistant microcontroller (often certified to Common Criteria EAL5+ or higher) with its own CPU, memory, and cryptographic engine. Found in smartcards, passports, and many hardware wallets.
- Embedded Secure Element (eSE) — the same concept soldered directly onto a device's mainboard, used by phones for payments.
- StrongBox / Secure Enclave — platform-specific secure subsystems (Android StrongBox, Apple Secure Enclave, Samsung Knox Vault) that store keys and enforce rate limits outside the main processor.
- Trusted Execution Environment (TEE) — an isolated execution zone inside the main CPU. Faster and cheaper than a dedicated SE, but with a larger attack surface.
- Hardware Security Module (HSM) — enterprise-grade key custody, typically used for institutional wallets and custodians.
What they share is the important part: an isolated execution environment, a true random number generator, protected key storage, and active tamper detection.
What Secure Chip Verification Actually Proves
During recovery, the chip performs several distinct jobs. It helps to separate them clearly.
1. Device and App Authenticity
The chip holds a unique, non-exportable device key and a hardware-backed attestation certificate. When you launch a recovery, the app requests an attestation. The chip signs a statement describing the device model, firmware version, and security patch level. If the signature fails to chain to the vendor's root of trust, the app refuses to continue.
Benefit: a counterfeit app on a rooted device cannot fake a genuine attestation, so it cannot silently capture your seed through the official flow.
2. Sealed Storage of the Seed and Derived Keys
Once the mnemonic is validated and the seed is derived, the seed is wrapped (encrypted) with a key that exists only inside the chip. The wrapped blob can be stored on disk, in a cloud backup, or on removable media — but it is useless without that specific chip.
Benefit: a stolen backup file, a stolen phone image, or a synced folder no longer equals a stolen wallet.
3. Integrity Verification of the Recovery Payload
Encrypted wallet backups, social-recovery shares, and multi-signature descriptor files can all carry authentication tags. The chip verifies these tags before the data is used. If even one byte is altered, the operation aborts.
Benefit: tampering and corruption are detected before a malformed key is written into your wallet.
4. User Presence and Authorization Binding
The unwrap key is gated behind a PIN, passcode, or biometric check that happens inside the secure world. The biometric template itself never leaves the chip. Critically, the chip enforces a hardware-enforced attempt counter: after a fixed number of failed PIN attempts, the key material is permanently destroyed rather than being retryable.
Benefit: offline brute-force attacks on a stolen device become economically pointless.
5. Trusted Randomness and Key Derivation
The chip supplies entropy from a true random number generator and can perform PBKDF2, HKDF, or BIP-32 derivation internally using an HMAC engine. The seed never has to be assembled in general-purpose memory.
Benefit: deterministic wallets are reproduced exactly, without exposing intermediate secrets to the host OS.
The Recovery Flow, Step by Step
Here is what a properly implemented secure-chip recovery looks like in practice.
Step 0 — Before You Start
- Confirm you have the correct mnemonic and the correct derivation path (BIP-44, BIP-84, BIP-86, and so on). A correct phrase with the wrong path restores the wrong wallet.
- Make sure the device is charged and offline if the wallet supports it.
- Have a second, independent record of the recovery phrase available for verification.
Step 1 — Verify the Device Security State
The app queries the secure chip for an attestation report. On Android this is a hardware-backed Key Attestation; on Apple platforms, it is a Secure Enclave attestation. You should see:
- Verified boot state (not rooted, not jailbroken)
- Security patch level within an acceptable window
- A hardware-backed key that is marked non-exportable
If any of these fail, stop. Do not type a seed phrase into a device you cannot verify.
Step 2 — Enter the Mnemonic in a Protected Context
The phrase is typed into a recovery screen that runs in a hardened environment: no clipboard access, no screenshots, no autofill, no accessibility overlays, and no third-party keyboard. Input is streamed directly to the secure world.
Step 3 — Validate and Derive Inside the Chip
The chip performs checksum validation (BIP-39 wordlist and checksum bits), expands the mnemonic with the optional passphrase, and derives the master seed. The plaintext seed exists only within the chip's protected memory.
Step 4 — Seal the Result
The derived keys are wrapped under a chip-bound key and written to persistent storage. The unwrapped plaintext is zeroized from volatile memory. Some implementations also generate a fresh hardware-backed recovery blob that can be stored off-device.
Step 5 — Confirm with a Hardware-Backed Challenge
A well-designed wallet asks the chip to sign a challenge with the restored key and verifies the signature against the expected address. This proves the recovery produced the correct key, not merely a key.
Step 6 — Migrate or Lock Down
Optionally, the recovered keys are re-derived under a new chip-bound key on a new device, then the old sealed blob is destroyed. This is the safest way to move a wallet after a device compromise.
Platform Comparison at a Glance
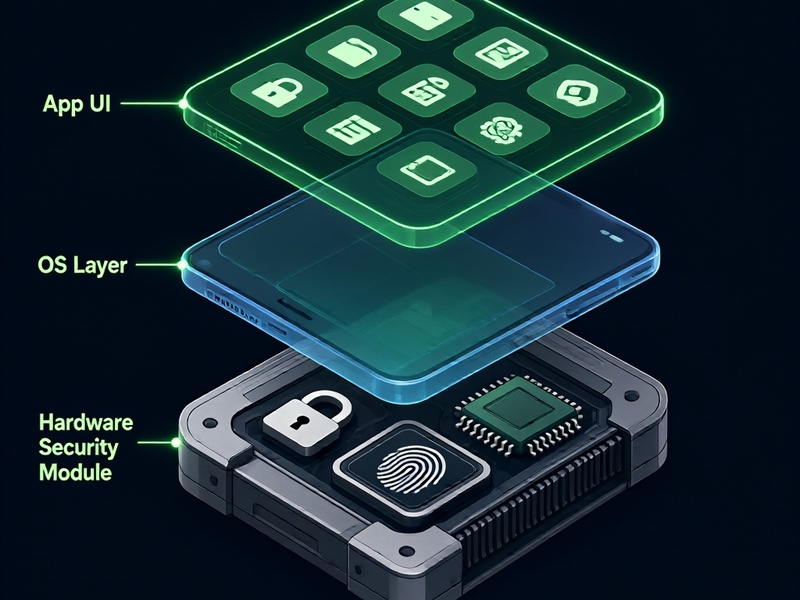
- Dedicated secure element (hardware wallets): strongest isolation, PIN enforced in silicon, seed never touches a general-purpose CPU. Slower setup and manual backup.
- StrongBox / Secure Enclave (phones): excellent convenience, hardware-backed attestation and rate limiting, but depends on vendor firmware and OS updates.
- TEE-only implementations: faster and more widely available, but a larger trusted computing base means a larger theoretical attack surface.
- Software-only wallets: no hardware root of trust. Attestation cannot be verified, and keys live in the same memory as everything else.
Where Secure Chips Still Do Not Help
Be honest about the limits:
- They cannot protect a seed you typed into a compromised app on a different device. If the phrase was exposed once, it is compromised forever.
- They cannot fix a bad backup. If you lost the mnemonic, the chip cannot recover your funds.
- They cannot prevent social engineering. Someone convincing you to read out your words bypasses every hardware control.
- They cannot guarantee flawless firmware. Hardware vulnerabilities and supply-chain attacks are rare but real; keep firmware updated and buy from official sources.
- They cannot protect you from yourself on the same device. Malware that injects a fake recipient address into a transaction still wins, even with perfect key custody.
Best Practices Checklist
- Verify hardware attestation before entering any seed phrase.
- Never type a mnemonic into a device you do not physically control.
- Prefer a dedicated secure element over a TEE-only implementation for large holdings.
- Use a strong, unique PIN. Remember that a hardware attempt counter will eventually wipe the keys — that is a feature, not a bug.
- Test your recovery process with a small amount before trusting it with your full balance.
- Store your mnemonic offline, on metal or paper, in more than one geographic location.
- Keep firmware current, and treat every recovery prompt as hostile until proven otherwise.
- After recovery, immediately re-seal keys under the new device's chip and securely erase any old sealed backups.
The Bottom Line
Secure chip verification turns wallet recovery from a leap of faith into a verifiable, hardware-enforced process. The chip proves the device is genuine, keeps the seed out of general-purpose memory, rate-limits brute-force attempts in silicon, and seals the derived keys so a stolen backup is worthless on its own.
It is not magic, and it does not forgive a leaked seed phrase. But when combined with disciplined backup habits and careful verification steps, it removes the most common and most costly failure modes from the recovery process — the ones that have emptied thousands of wallets.
Verify the hardware. Then enter the words.